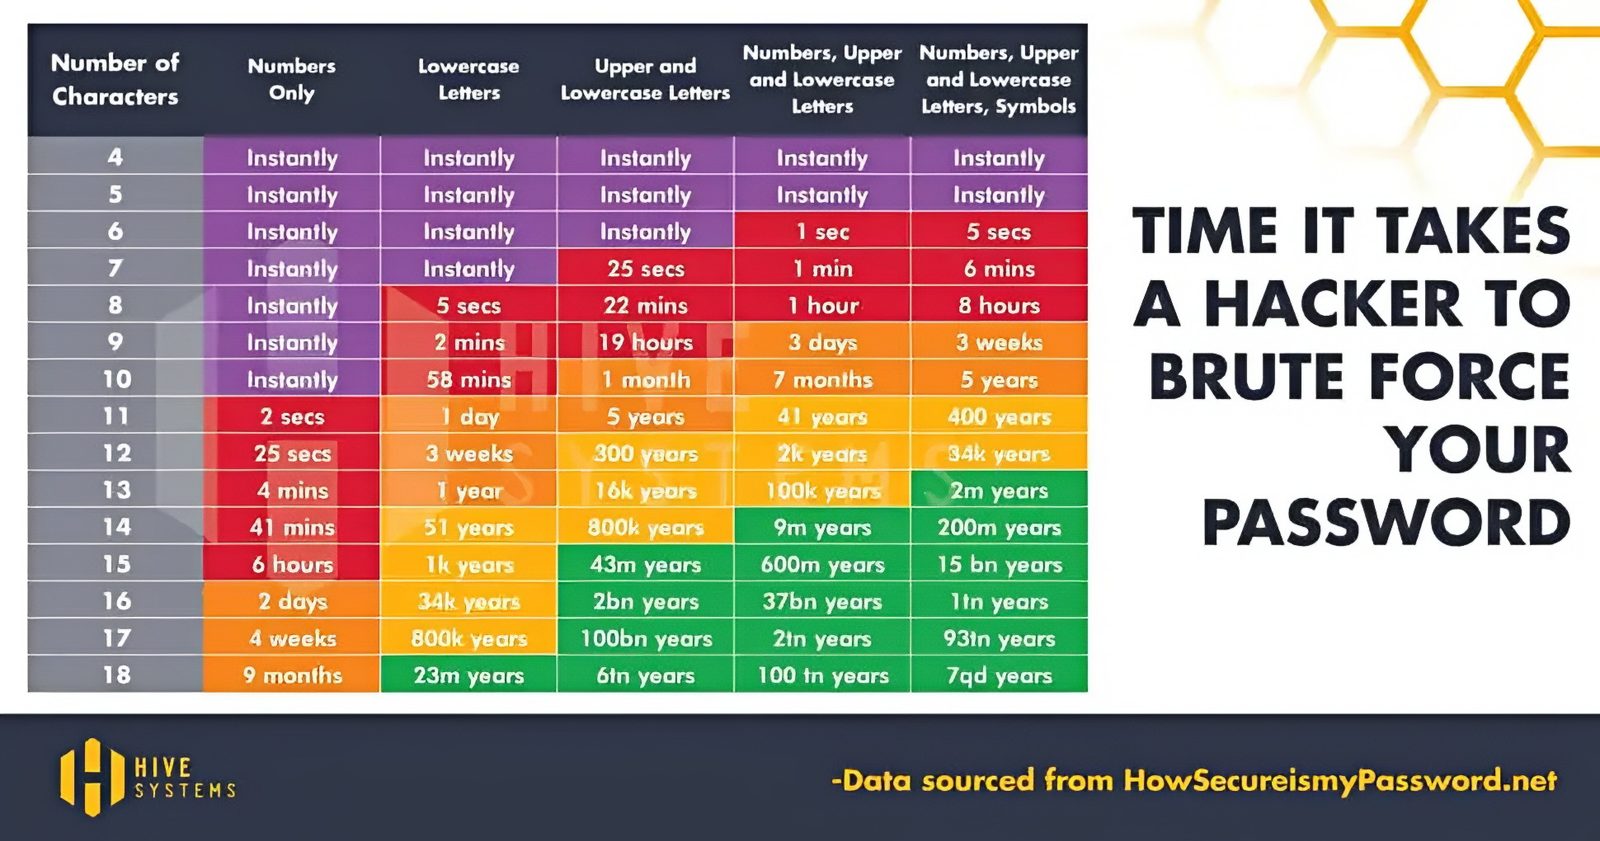
Brute force attacks are particularly effective against weak passwords. A strong, complex password acts as a formidable barrier against such attacks. It should include a combination of uppercase and lowercase letters, numbers, and special characters. Remember, the longer and more unique your password, the harder it is for attackers to crack. According to Komando, if your password comprises numbers, upper and lowercase letters and symbols, it will take a hacker 34,000 years to crack – if it’s 12 characters long.
How the hackers find your vulnerable website:
Step 1 – Target Selection
- The attacker identifies a target, such as a user account, network, or system, that they want to compromise. Most attacks in WordPress are done at random. Websites are typically discovered from shared servers and domain databases. There is a Linux program that will look for vulnerable websites, it is a tool for web developers to check their sites but of course, hackers use it too, the tool can automatically list all user accounts withing that website.
Step 2 – Enumeration
- Before launching the brute force attack, the hacker performs enumeration to gather information about the target, such as valid usernames, email addresses, or system details.
Step 3 – Password Guessing
- The attacker employs specialized software or scripts to systematically guess passwords. There are different methods at guessing a password. The most popular method is a dictionary attack, which involves using precompiled dictionaries of commonly used passwords. These dictionaries may include words from various languages, character substitutions, and common phrases. This can involve trying every conceivable combination, starting from the simplest and most common passwords to more complex ones.
There are many FREE sites for creating random passwords. My favourite one is the Kaspersky FREE PASSWORD GENERATOR 🙂
Free Password Generator | Strong & Random Passwords
I hope you find this useful.
Discover more from Mobile PC Rescue
Subscribe to get the latest posts sent to your email.